Auto Spare Tires
2026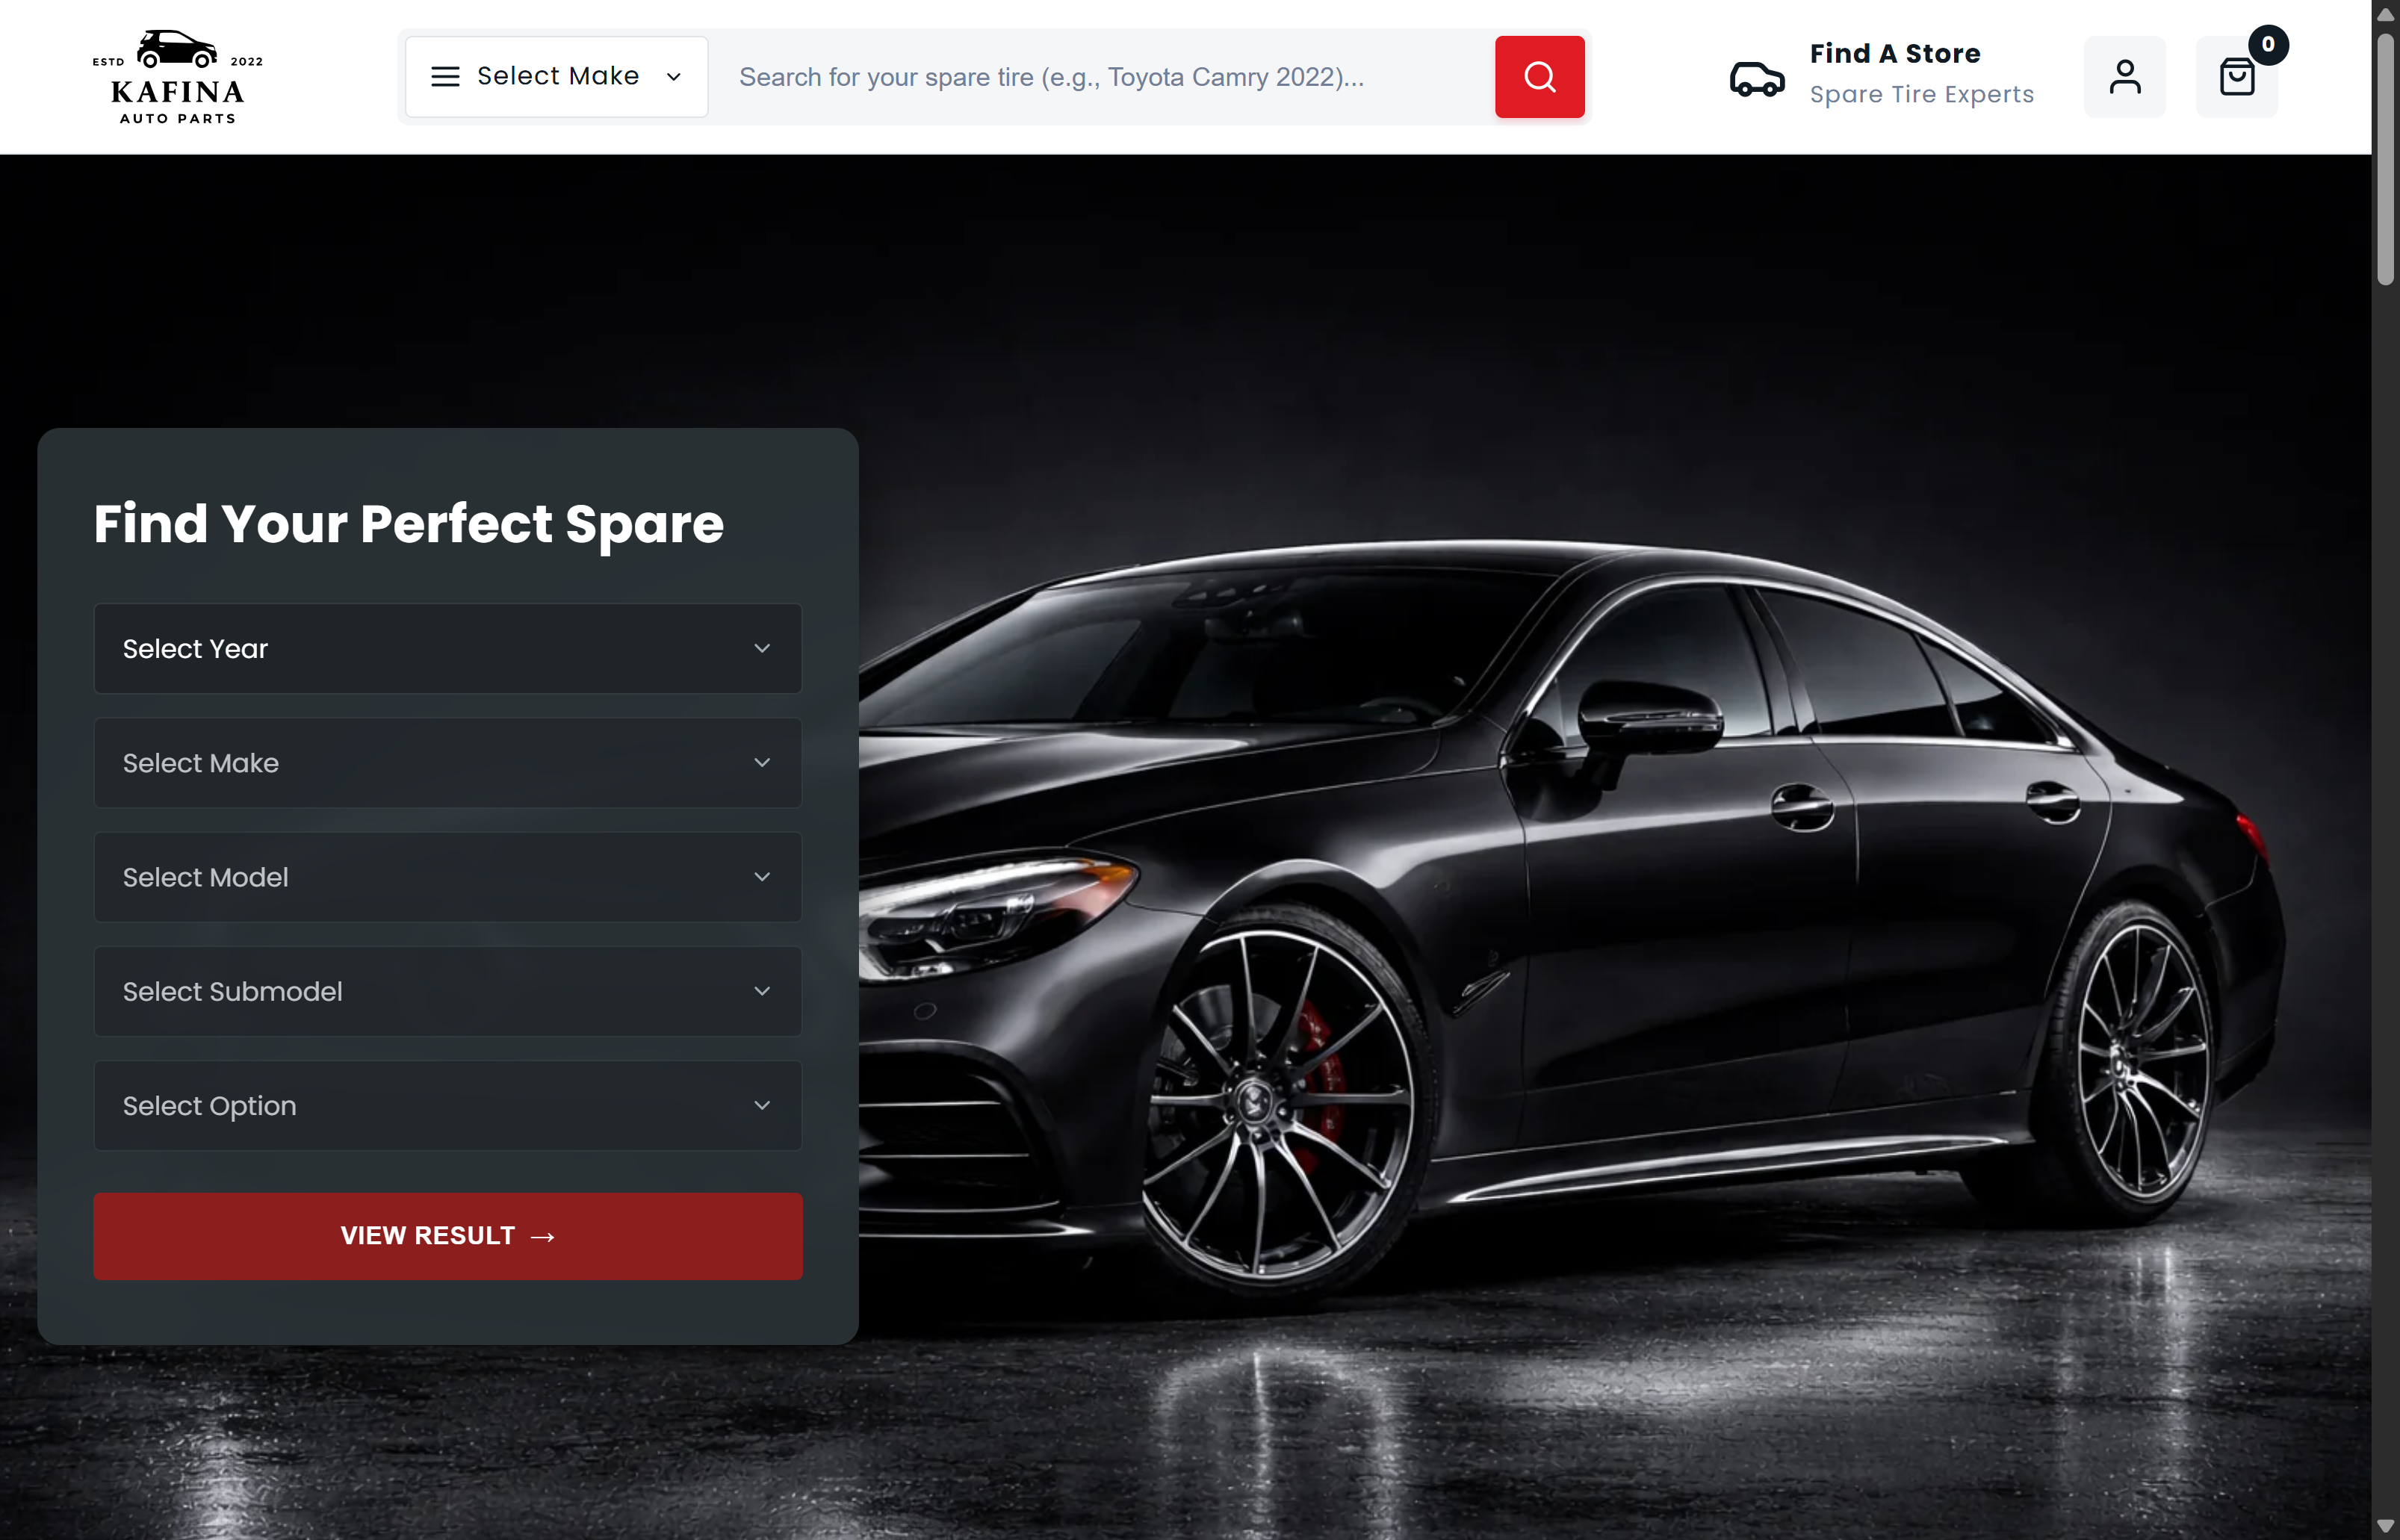
Auto Spare TiresCommerce
Vehicle-fitment spare catalog
Fitment lived in a parts specialist’s head. We shipped a year / make / model / submodel selector in front of the spare-tire catalog.
commerce
Learn more 
Not a theme. Not a stack we already liked. A system that matches how the business actually runs.
Product Software · Marketplaces · Internal Tools · Commerce · Automation
Fitment lived in a parts specialist’s head. We shipped a year / make / model / submodel selector in front of the spare-tire catalog.
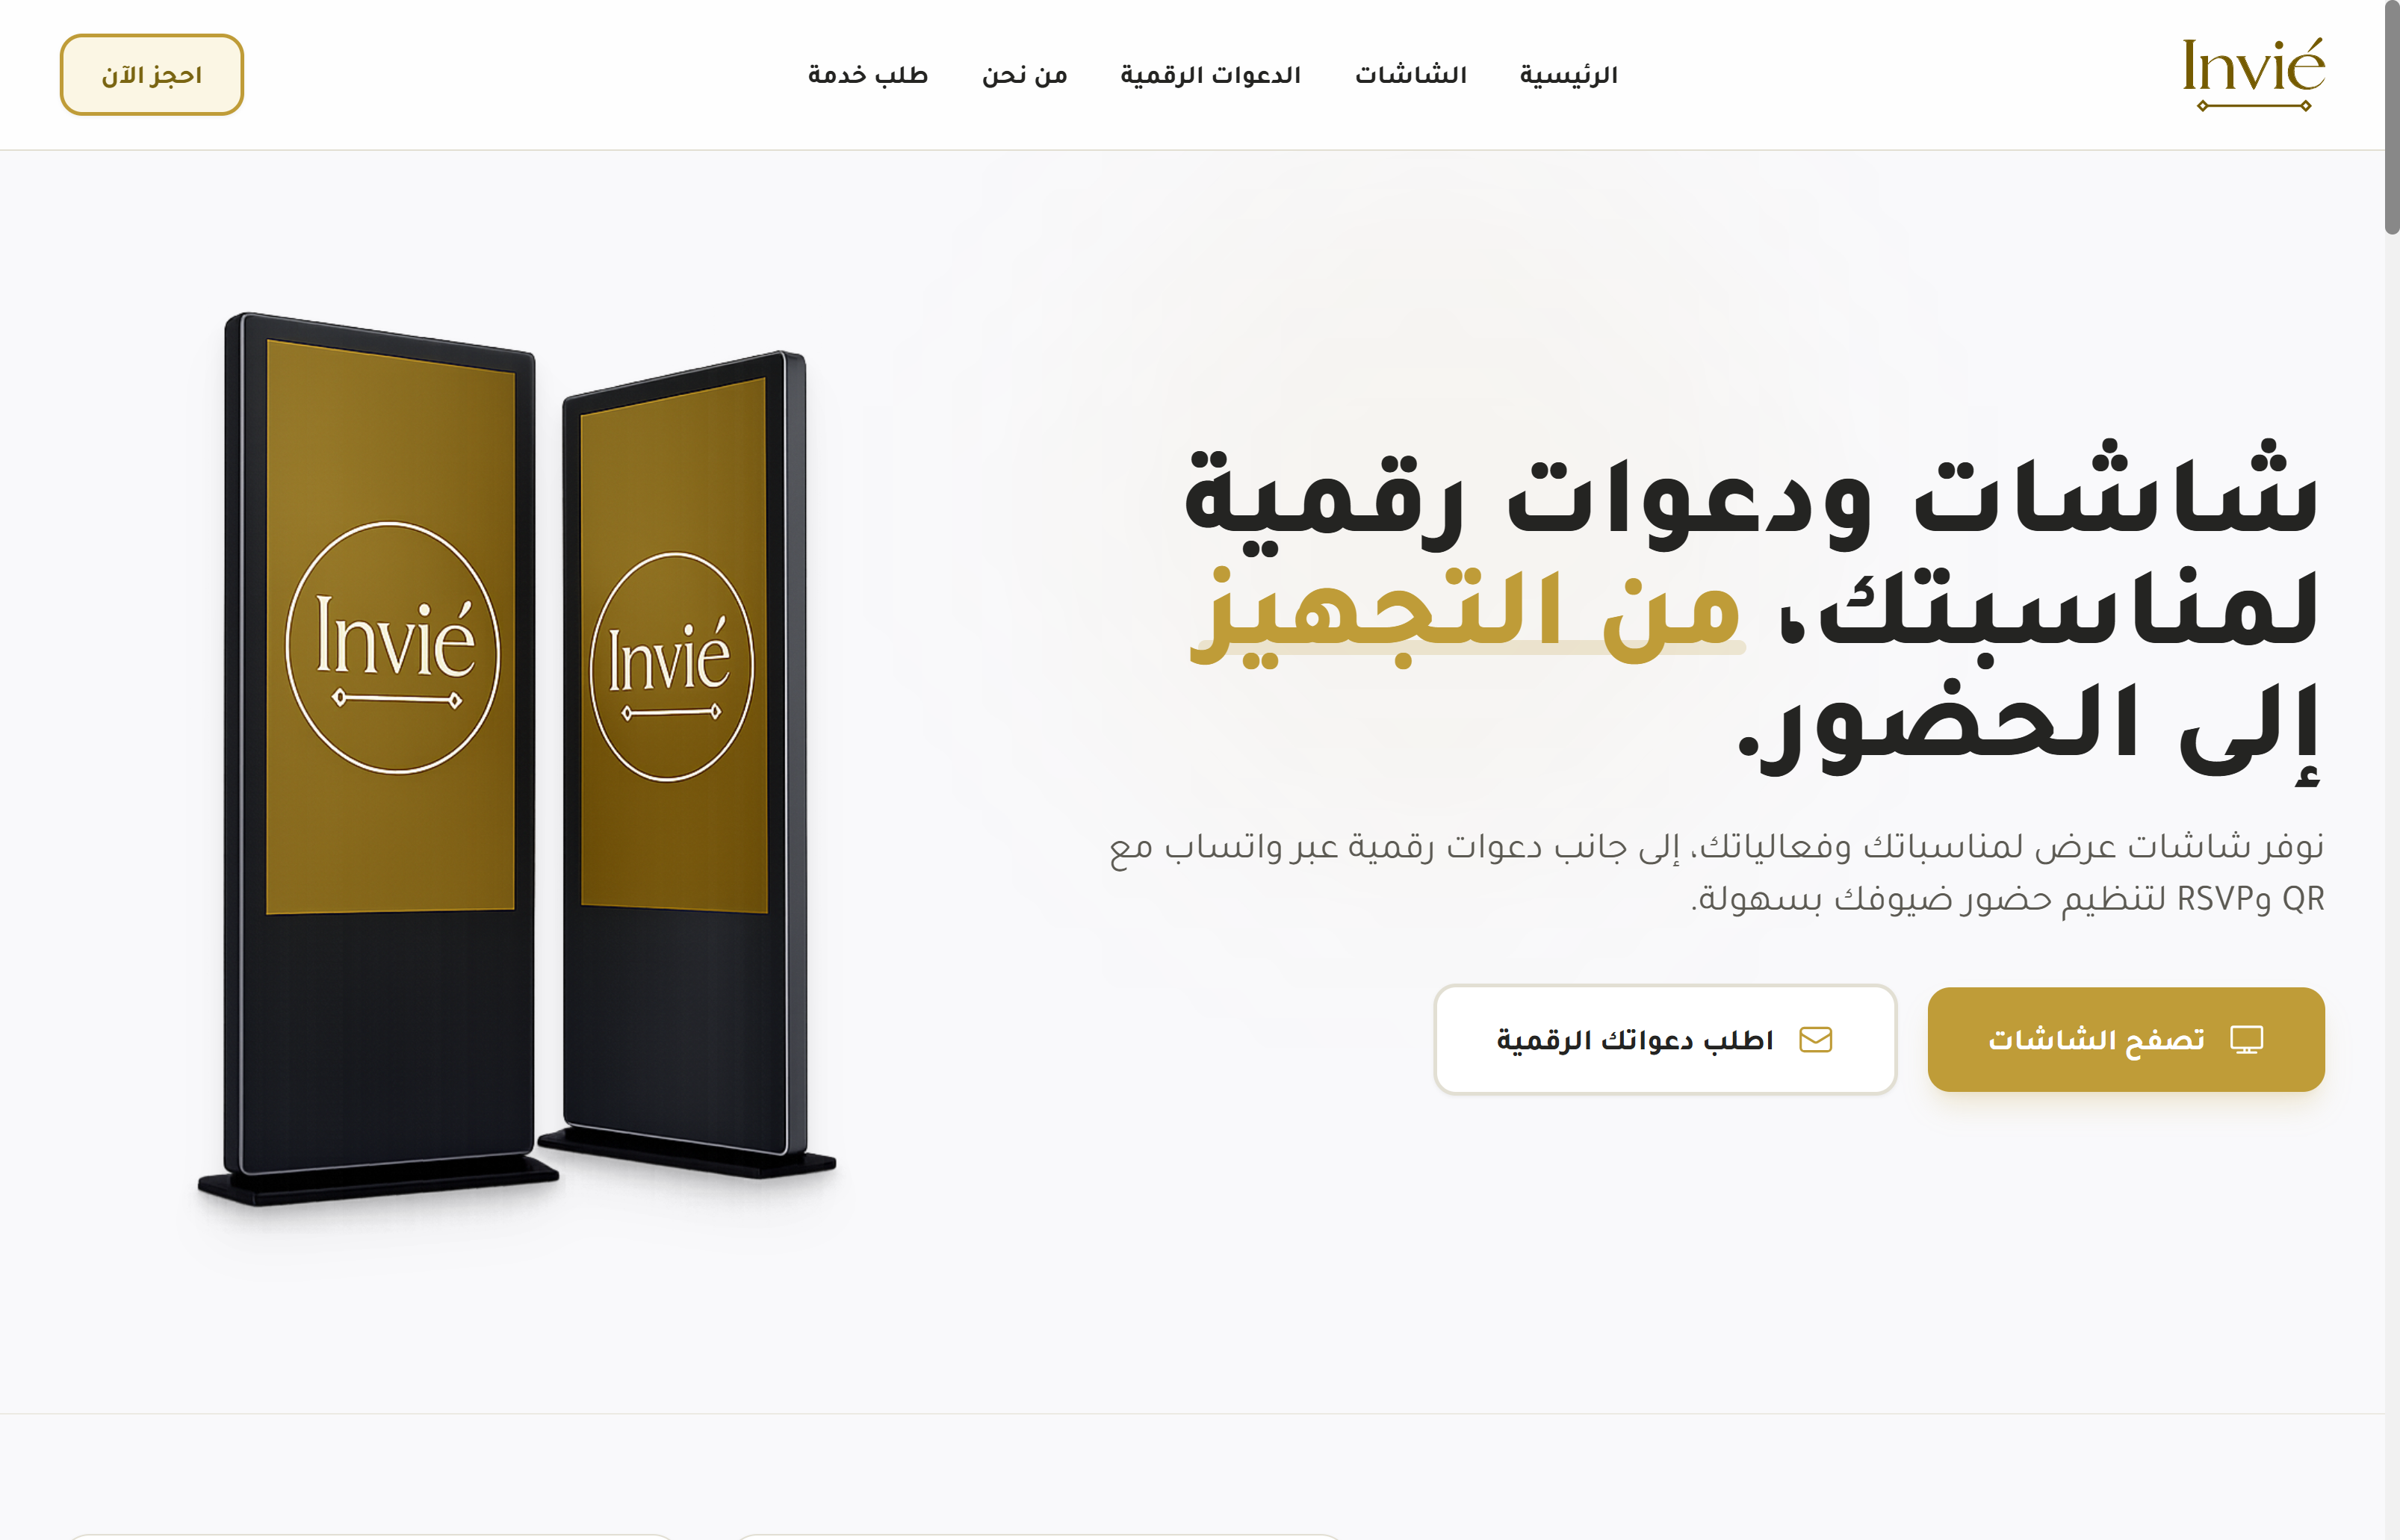
Screen rental and guest lists were two vendors. We shipped one platform for renting display hardware and sending WhatsApp invitations with QR and RSVP.
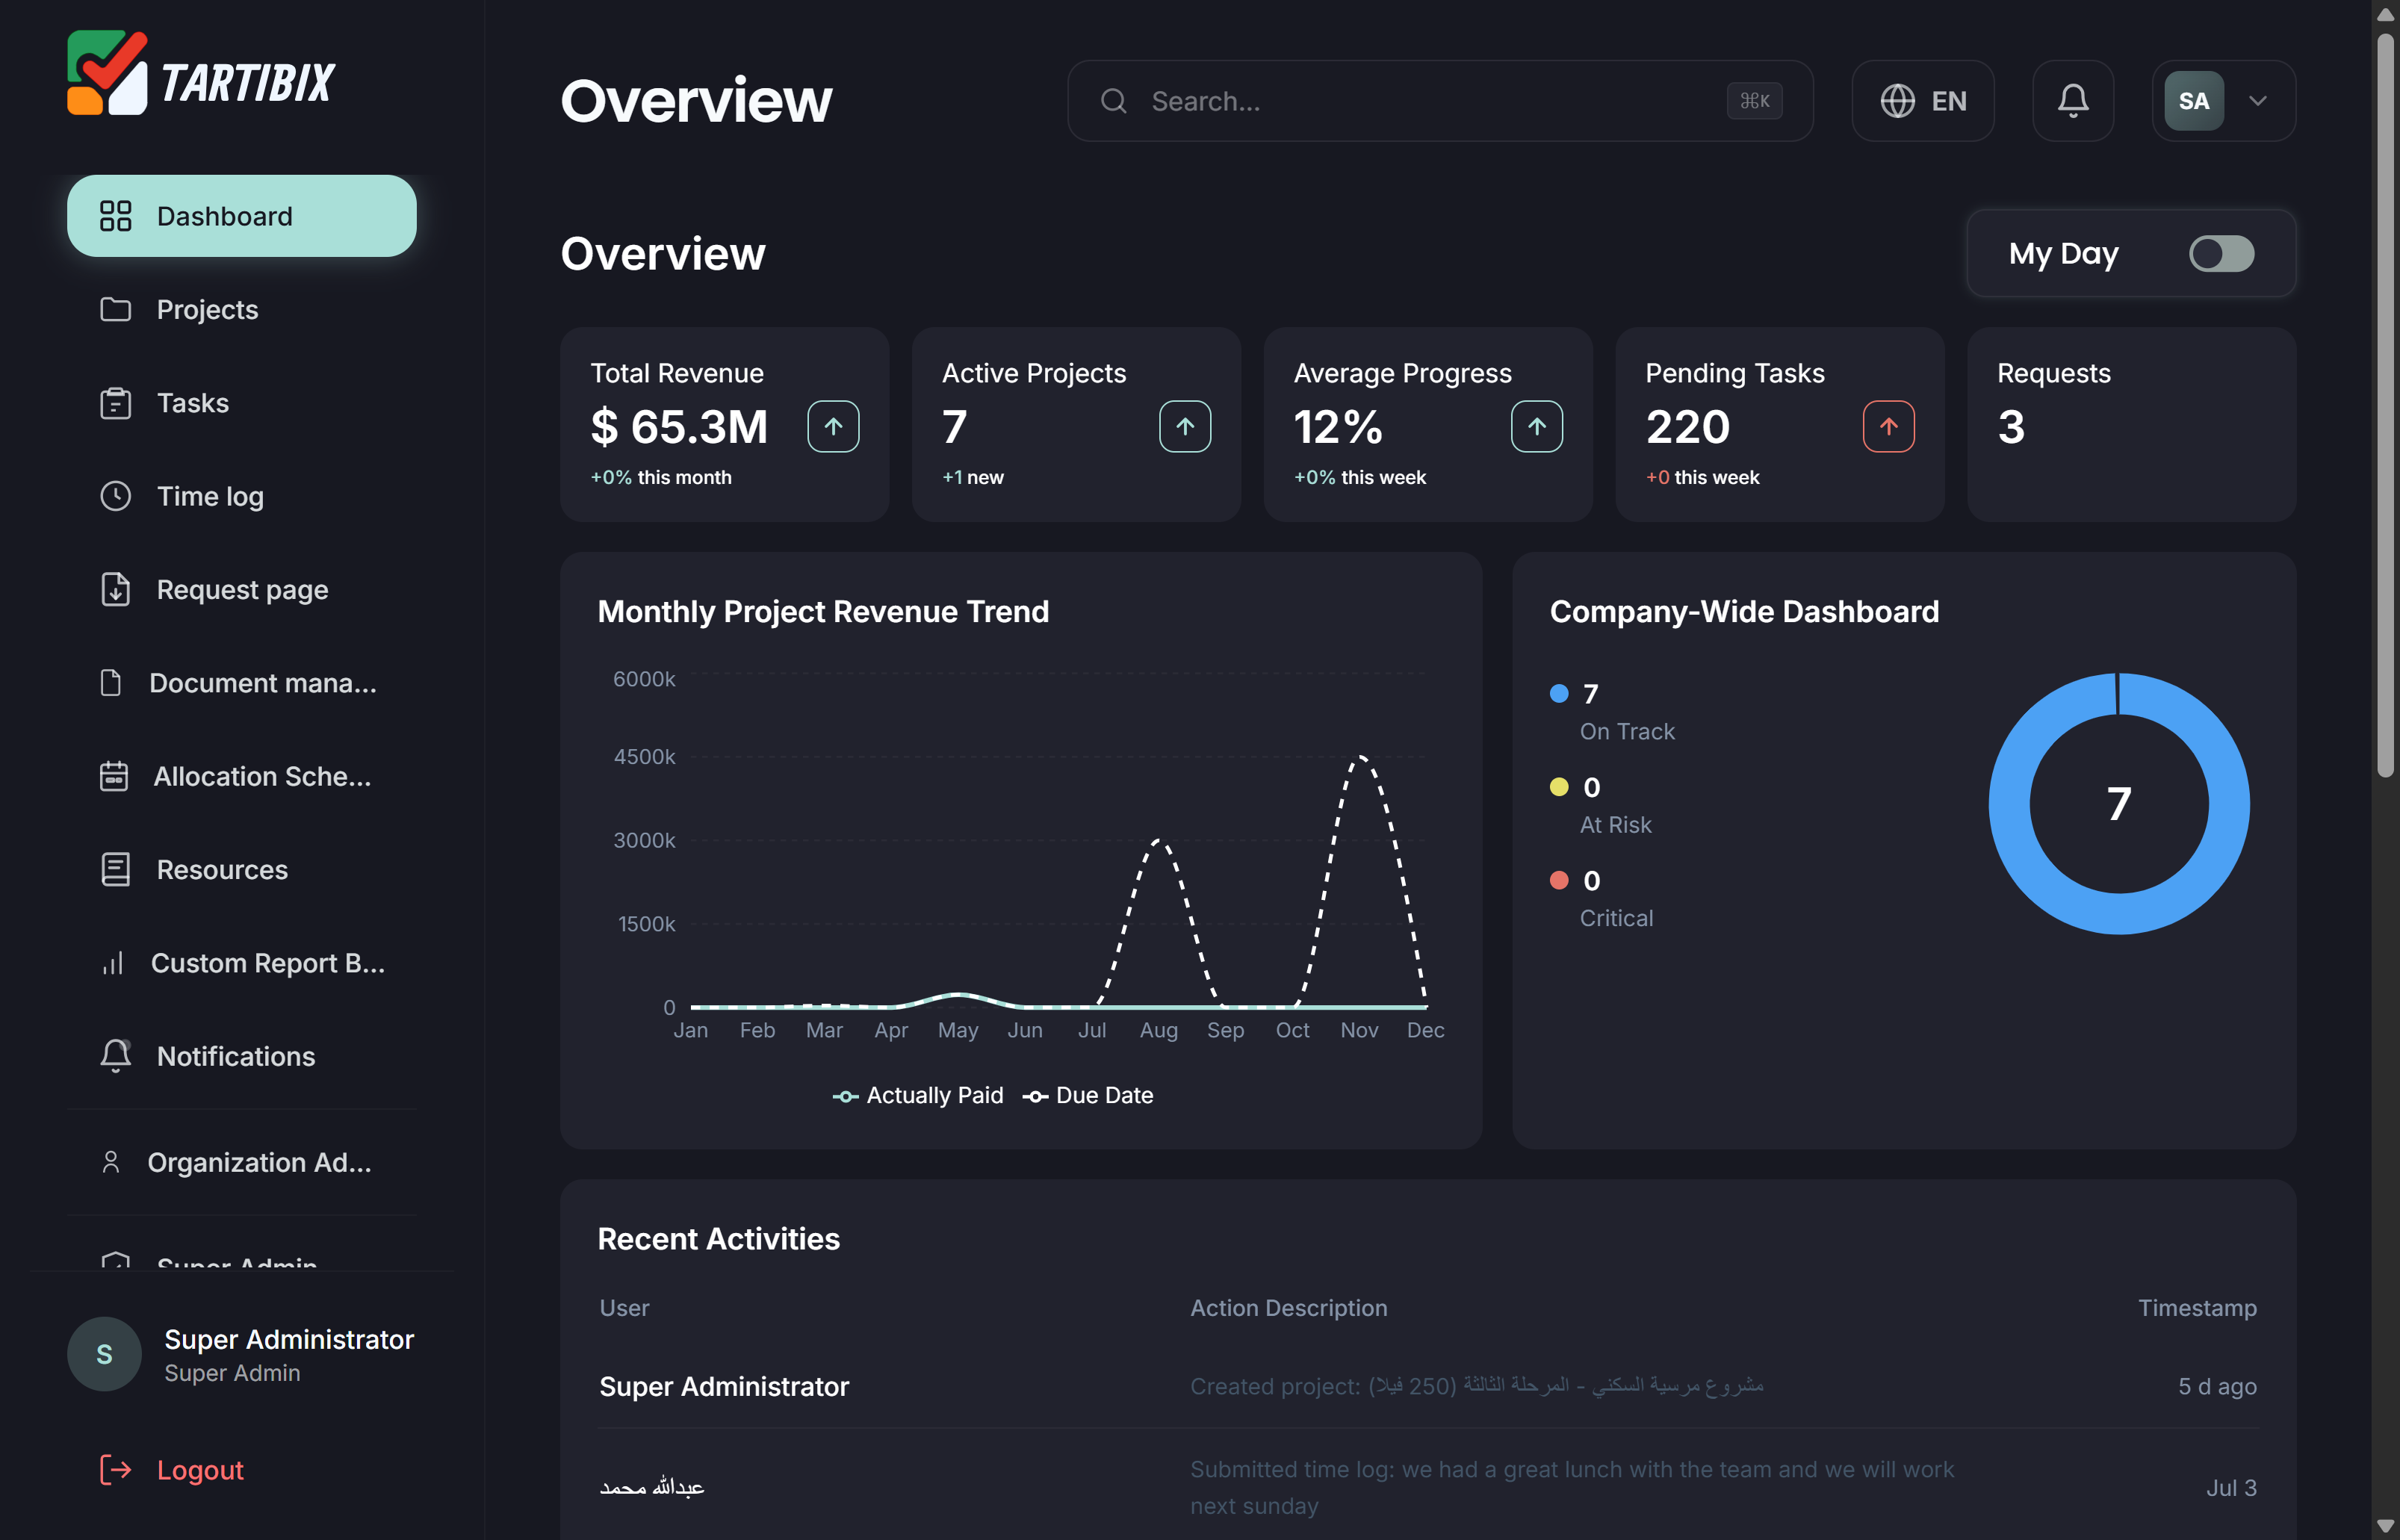
Construction coordination was files and group chats. We shipped a logged-in resource hub for tasks, teams, and project delivery.
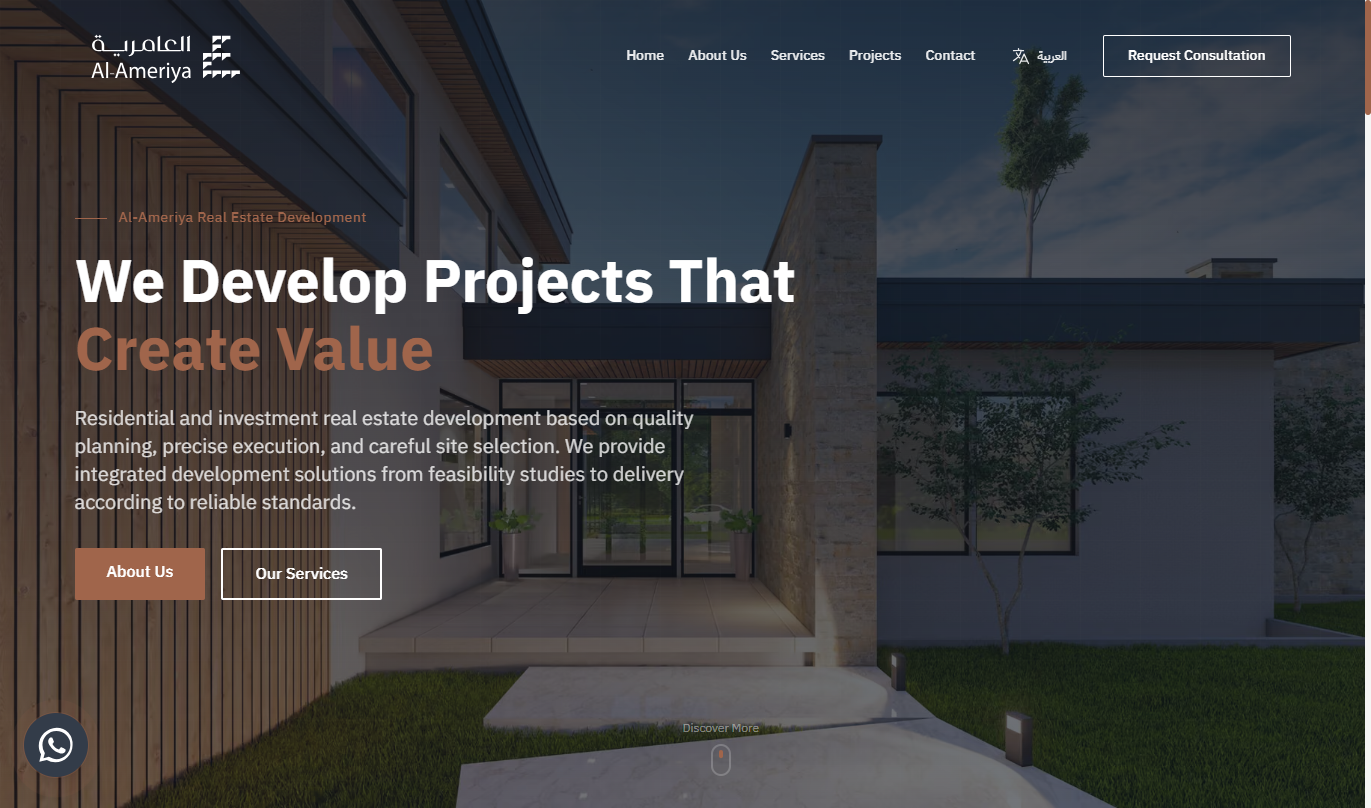
Development work was a paragraph in a company profile. We shipped a bilingual developer site that separates development, project control, opportunity study, and marketing.
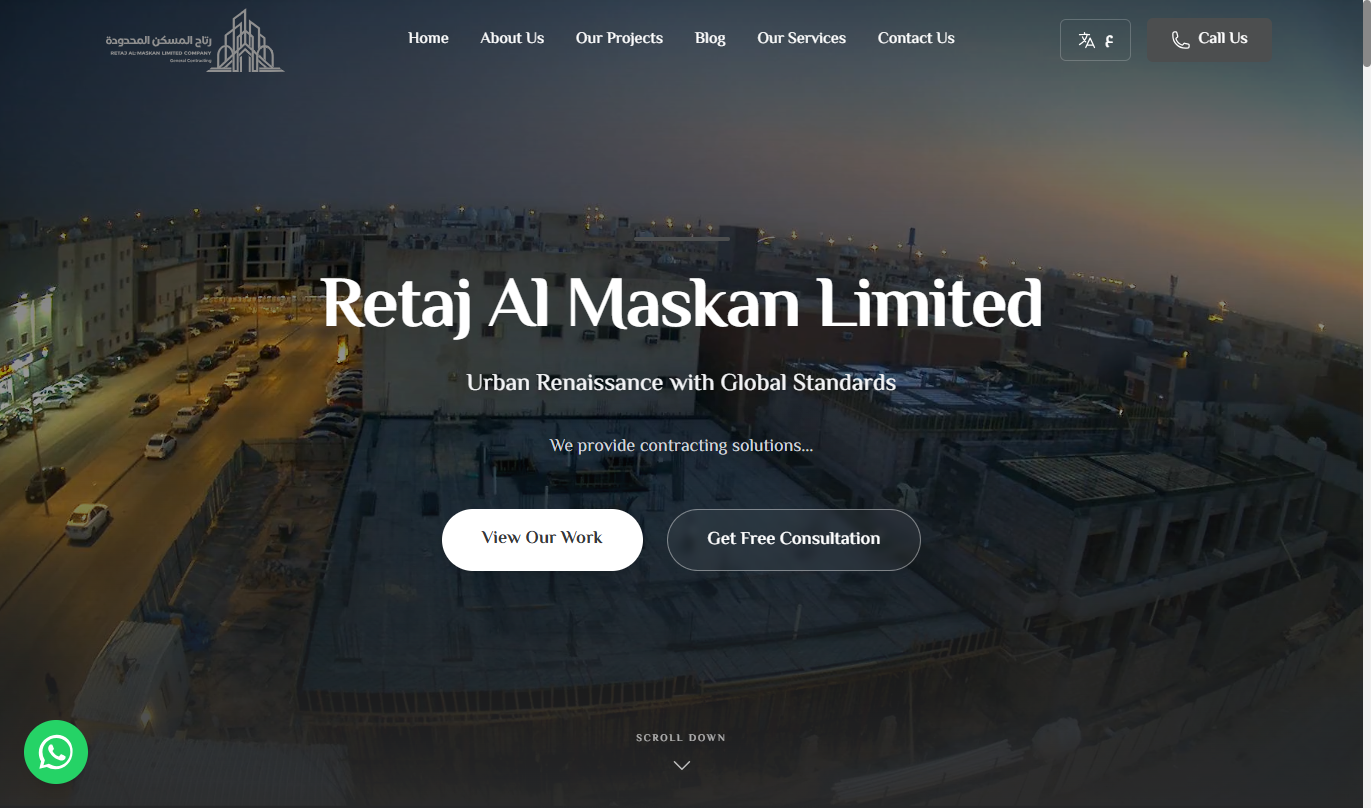
A luxury contractor’s record lived in site photos on phones. We shipped the corporate surface for vision, process, and consultation requests.
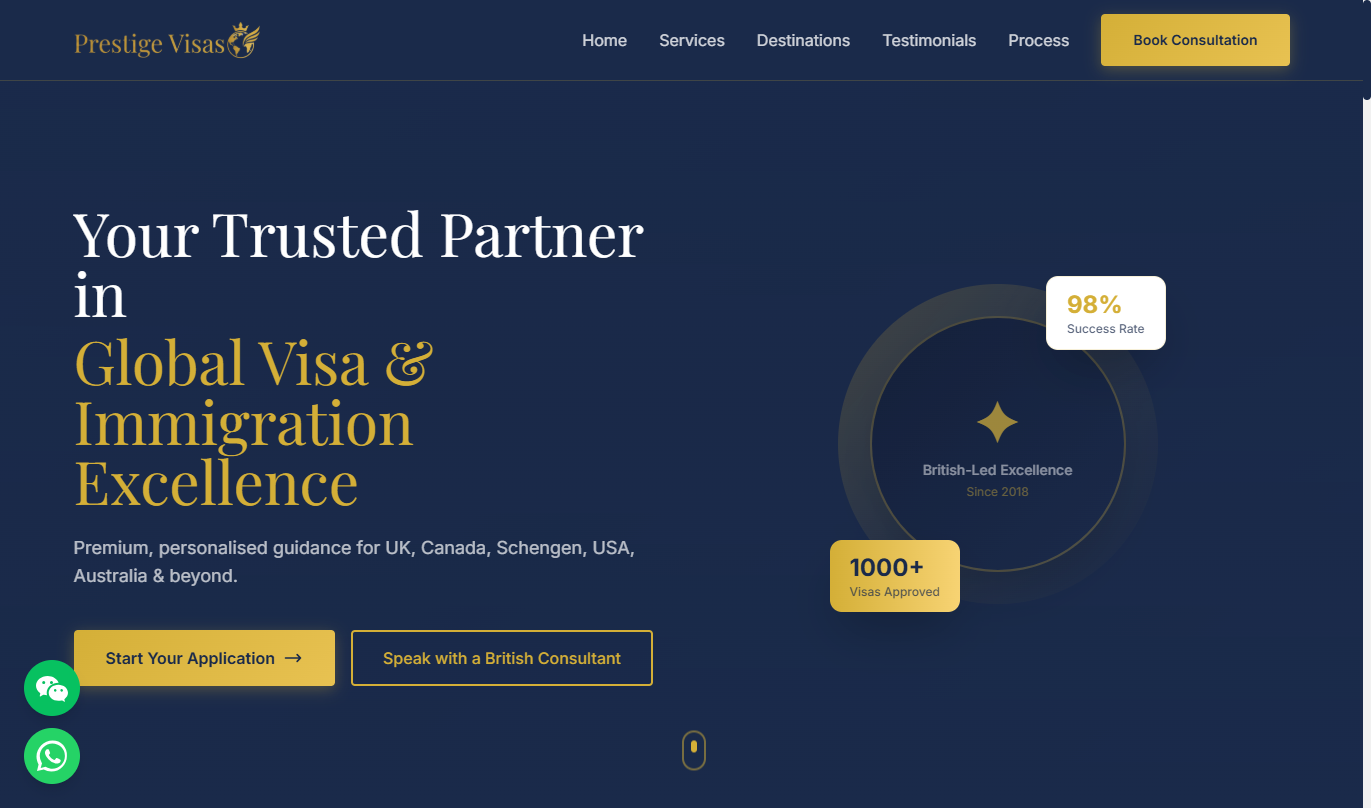
Visa work arrived as documents in email. We shipped a consultancy site that routes visitor, student, and PR cases into a consultation booking.
Access controls, cryptographic key lifecycle, and continuous log integrity.
Granular consent architecture, right-to-erasure workflows, zero untracked PII.
End-to-end ePHI encryption (AES-256), tamper-proof audit trails, session timeouts.
Kingdom data localization readiness, explicit processing consent, statutory rights.
Security is never an afterthought or a plugin bolted on before launch. We begin with structured threat modeling, least-privilege Role-Based Access Control (RBAC), parameter sanitization, and encrypted data flows across every database and third-party integration.
Every pull request is checked with automated Static Application Security Testing (SAST) and software dependency vulnerability monitoring (SCA). Prior to delivery, we execute simulated offensive penetration tests against the OWASP Top 10 to eliminate injection, broken auth, and IDOR flaws.
Whether you operate in the EU, the US, or Saudi Arabia, your platform is architected to satisfy external compliance audits on day one. We engineer compliant access logs, automated data retention schedules, strict sovereignty controls, and user privacy rights without slowing delivery.
Over 80% of security breaches stem from social engineering and credential mishandling. Alongside clean software, we supply your team with operational security hygiene runbooks, automated secrets rotation guides, and employee awareness best practices for lasting defense.
Security is never an afterthought or a plugin bolted on before launch. We begin with structured threat modeling, least-privilege Role-Based Access Control (RBAC), parameter sanitization, and encrypted data flows across every database and third-party integration.
Every pull request is checked with automated Static Application Security Testing (SAST) and software dependency vulnerability monitoring (SCA). Prior to delivery, we execute simulated offensive penetration tests against the OWASP Top 10 to eliminate injection, broken auth, and IDOR flaws.
Whether you operate in the EU, the US, or Saudi Arabia, your platform is architected to satisfy external compliance audits on day one. We engineer compliant access logs, automated data retention schedules, strict sovereignty controls, and user privacy rights without slowing delivery.
Over 80% of security breaches stem from social engineering and credential mishandling. Alongside clean software, we supply your team with operational security hygiene runbooks, automated secrets rotation guides, and employee awareness best practices for lasting defense.
When investors, enterprise buyers, or regulatory bodies audit your platform, you won't scramble to rewrite your stack. You hand them clean compliance logs and a system tested against real attacks.
A marketplace that is getting messy. An internal process still living in Slack. A store that needs logic a theme cannot hold. A product that needs a technical partner, not another vendor waiting for tickets.
If you need a five-page brochure site by Friday, we are the wrong room. If you want us to start in a framework because a social thread recommended it, also the wrong room. We select the architecture only after understanding the constraint.
If the problem is real, write to us. If it is still a slogan, it will not survive the first call.